-
Inside a multi stage toll fraud operation targeting Poland
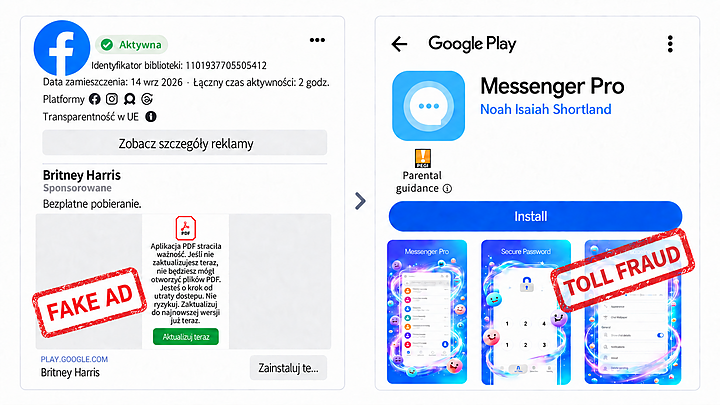
CERT Polska uncovered a toll fraud operation targeting Polish users through deceptive Meta advertisements and malicious applications distributed via Google Play. We preserved 1235 ads, linked 852 to 17 applications through code or infrastructure, reconstructed the complete execution chain, and observed live premium SMS and carrier billing tasking.
Read more -
Analysis of cifrat: could this be an evolution of a mobile RAT?
CERT Polska analyzed a Booking themed Android malware chain delivered through phishing and a fake update website. The sample is a multistage dropper that installs a hidden accessibility controlled RAT with WebSocket C2.
Read more -
Analysis of FvncBot campaign
CERT Polska has analyzed an SGB-branded Android malware sample from the FvncBot campaign targeting Poland. The app installs a second-stage implant, coerces the victim into enabling accessibility, and registers the device to a backend that issues per-device credentials.
Read more -
Analysis of NGate malware campaign (NFC relay)
CERT Polska has observed new samples of mobile malware in recent months associated with an NFC Relay (NGate) attack targeting users of Polish banks.
Read more -
The Dark Knight Returns: Joker malware analysis
CERT Polska has recently observed new samples of the “Joker” mobile malware. The applications are present in the Google Play Store and target Polish users, among others.
Read more