-
Inside a multi stage toll fraud operation targeting Poland
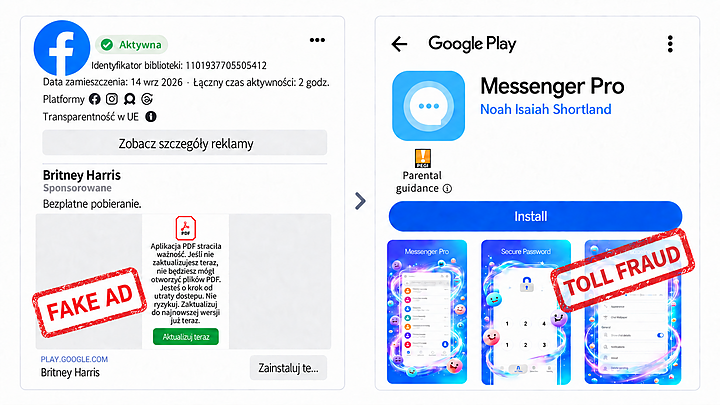
CERT Polska uncovered a toll fraud operation targeting Polish users through deceptive Meta advertisements and malicious applications distributed via Google Play. We preserved 1235 ads, linked 852 to 17 applications through code or infrastructure, reconstructed the complete execution chain, and observed live premium SMS and carrier billing tasking.
Read more -
MikroTrick: technical analysis, disclosure process, and the use of LLM agents
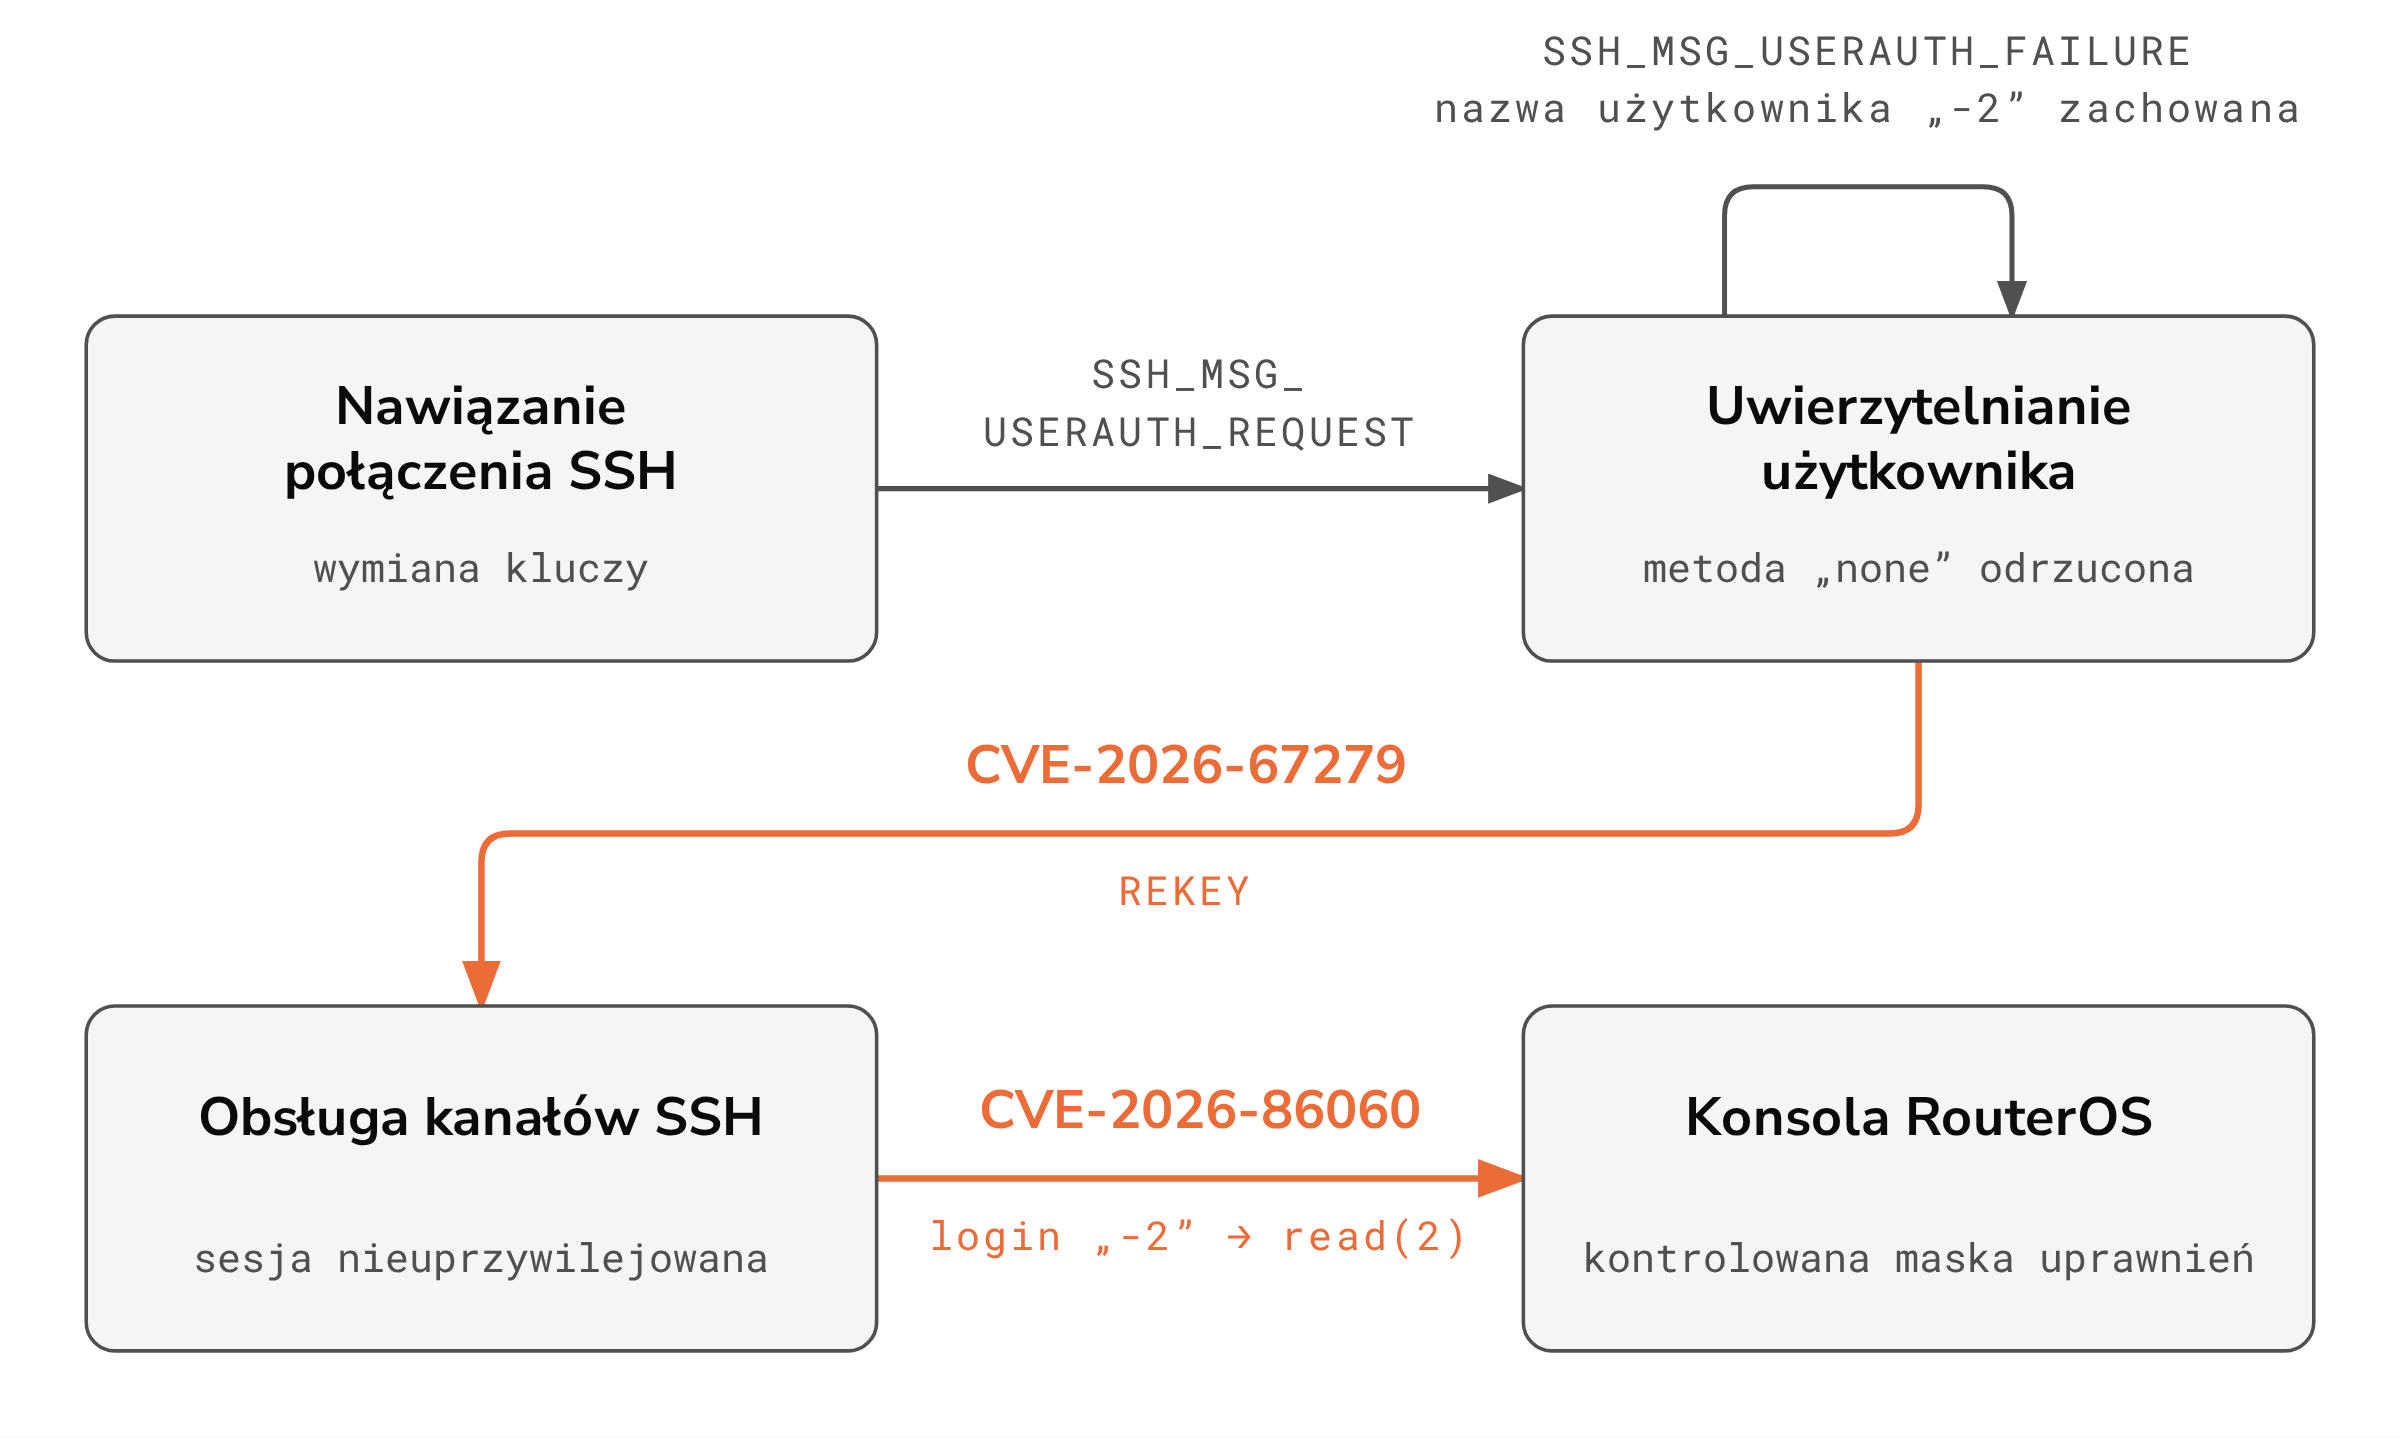
We describe the technical details of the MikroTrick chain, which combines the CVE-2026-67279 and CVE-2026-86060 vulnerabilities and, when chained, allowed full takeover of a device without authentication. We explain the mechanics of the attacks observed in the wild, the coordinated disclosure of both vulnerabilities, and the practical role of LLM agents in the RouterOS research.
Read more -
Analysis of cifrat: could this be an evolution of a mobile RAT?
CERT Polska analyzed a Booking themed Android malware chain delivered through phishing and a fake update website. The sample is a multistage dropper that installs a hidden accessibility controlled RAT with WebSocket C2.
Read more -
Analysis of FvncBot campaign
CERT Polska has analyzed an SGB-branded Android malware sample from the FvncBot campaign targeting Poland. The app installs a second-stage implant, coerces the victim into enabling accessibility, and registers the device to a backend that issues per-device credentials.
Read more -
ClickFix in action: how fake captcha can lead to a company-wide infection
We assisted a large organisation in the investigation and remediation of a live malware infection caused by a successful Fake Captcha attack. In this report, we summarize our observations and publish an in-depth malware analysis.
Read more -
Analysis of NGate malware campaign (NFC relay)
CERT Polska has observed new samples of mobile malware in recent months associated with an NFC Relay (NGate) attack targeting users of Polish banks.
Read more -
UNC1151 exploiting Roundcube to steal user credentials in a spearphishing campaign
CERT Polska is observing a malicious email campaign conducted by the UNC1151 group against Polish entities, exploiting a vulnerability in the Roundcube software.
Read more -
Deobfuscation techniques: Peephole deobfuscation
In this article we describe a basic deobfuscation technique by leveraging a code snippet substitution.
Read more -
The Dark Knight Returns: Joker malware analysis
CERT Polska has recently observed new samples of the “Joker” mobile malware. The applications are present in the Google Play Store and target Polish users, among others.
Read more -
Malware stories: Deworming the XWorm
XWorm is a multi-purpose malware family, commonly used as RAT. This post contains a detailed analysis and walk-through the reverse-engineering process.
Read more