-
MikroTrick: technical analysis, disclosure process, and the use of LLM agents
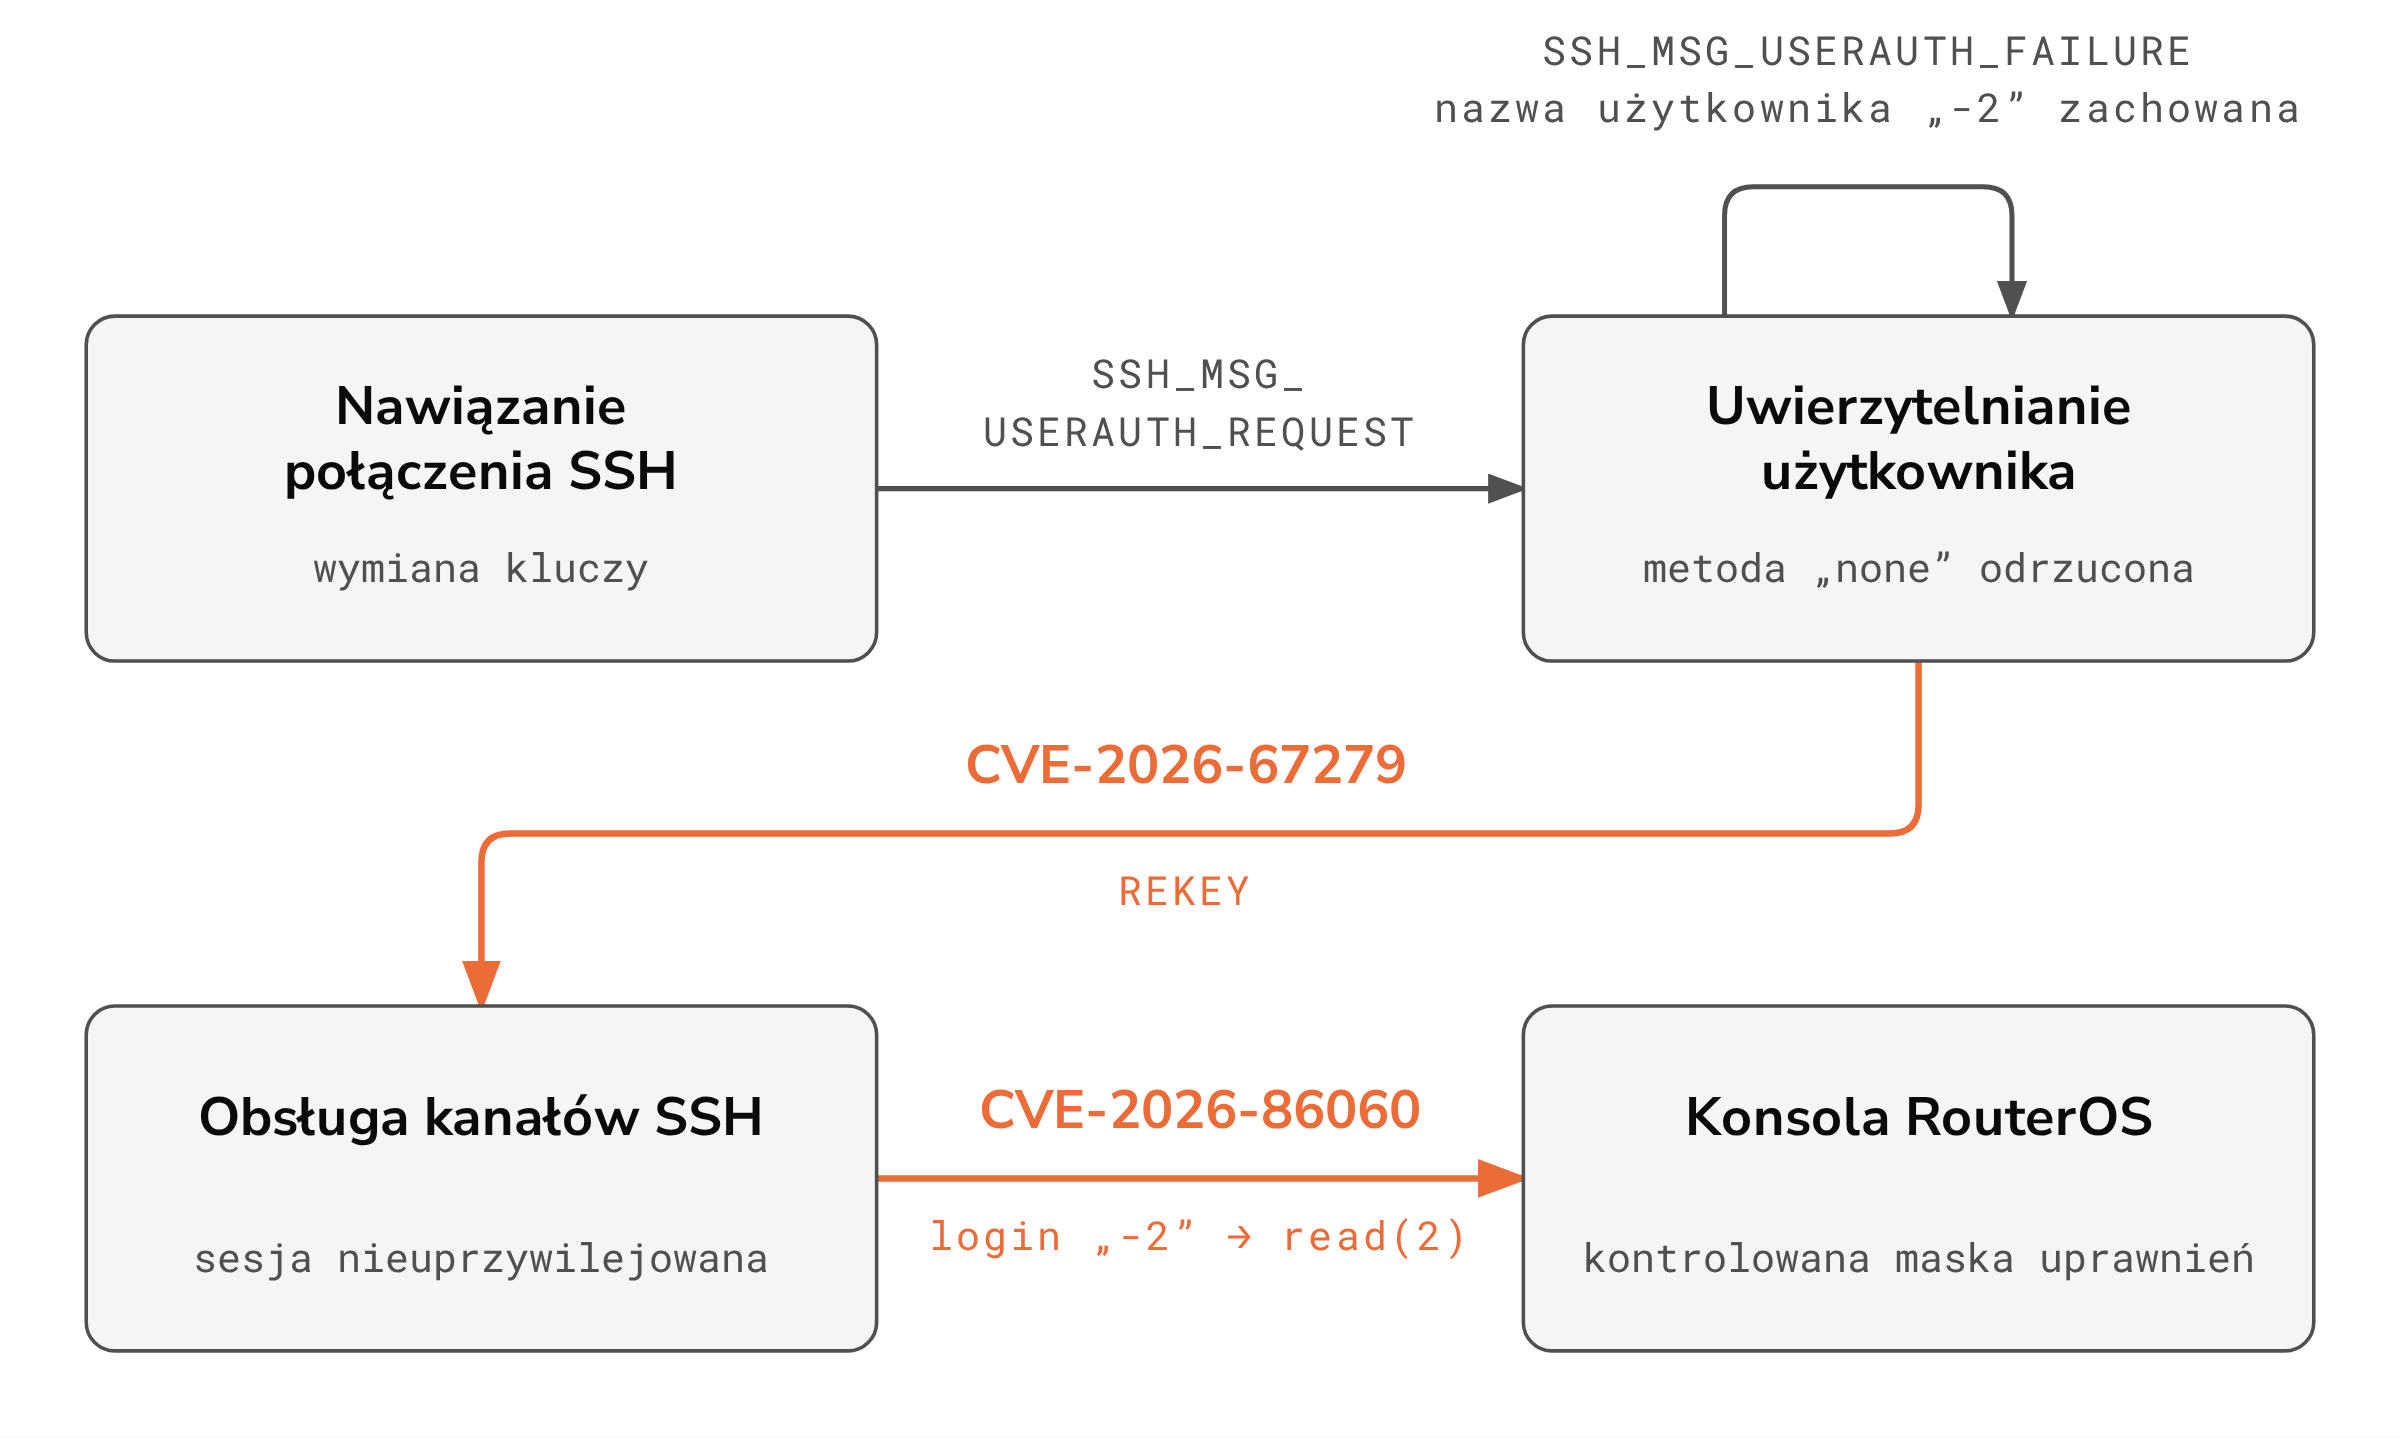
We describe the technical details of the MikroTrick chain, which combines the CVE-2026-67279 and CVE-2026-86060 vulnerabilities and, when chained, allowed full takeover of a device without authentication. We explain the mechanics of the attacks observed in the wild, the coordinated disclosure of both vulnerabilities, and the practical role of LLM agents in the RouterOS research.
Read more -
Critical vulnerabilities in MikroTik RouterOS are being actively exploited. Immediate update recommended
The CERT Polska team has identified and coordinated the disclosure of six vulnerabilities in MikroTik RouterOS, including two critical ones. The vulnerabilities are already being actively exploited to take over devices whose SSH service is accessible from the internet. We recommend immediately updating devices to the patched versions and verifying the configuration for signs of compromise.
Read more